CompTIA CySA+ CS0-004: What Actually Helps You Prepare for V4?


Preparing for the CompTIA CySA+ CS0-004 exam involves more than just watching courses, memorizing security terminology, and completing hundreds of practice questions.
CompTIA CySA+ CS0-004

The CS0-004 version introduces new considerations for exam preparation, particularly for candidates relying on study materials from older versions.

You need to find study resources that align with the current exam objectives and develop the judgment required to interpret evidence, investigate suspicious activity, and propose appropriate responses. A large volume of study material does not guarantee effective preparation; what matters most is whether your study method exposes your weaknesses and helps you articulate the rationale behind your decisions.

What Changed With CS0-004—and What Should You Check?

As the certification transitions from CS0-003 to CS0-004, verifying the version is a crucial first step. You should rely on CompTIA’s official certification documentation and the latest exam objectives rather than simply depending on course publication dates, retailer descriptions, or advice from those who took the previous version of the exam.

Be sure to start with the official CompTIA CySA+ certification page to obtain the exam objectives for the specific exam you plan to take. Use these objectives as a checklist when evaluating various courses, books, lab exercises, and practice tests. Pay close attention to the exam code, the covered domains, and the specific exam objectives; do not assume content is up-to-date simply because a resource is labeled “CySA+.”

Older materials are not automatically useless. Core concepts such as interpreting security logs, understanding vulnerabilities, investigating incidents, and evaluating security controls remain relevant to cybersecurity analysis. The risk is assuming that a resource covering familiar concepts necessarily covers the entire current exam. If you already own CS0-003 materials, identify the gaps against the CS0-004 objectives before deciding whether you need a replacement.

That approach protects both your study time and your budget. Rather than starting over because a new version exists, you can preserve useful knowledge while directing additional effort toward topics your existing resources do not adequately address.

Knowing the Terms Isn’t the Same as Analyzing the Evidence

CySA+ tests the reasoning behind a security decision, not just your ability to recognize terminology. The CS0-004 exam includes multiple-choice and performance-based questions, with up to 85 questions in 165 minutes and a passing score of 750 on a scale of 100–900. These details are reported in current exam-preparation materials; verify them against the official documentation before your appointment.

Consider a hypothetical scenario: a SIEM dashboard reports several failed logins followed by a successful authentication from an unfamiliar IP address. A candidate who memorizes security terminology might immediately label the event a brute-force attack. An analyst would look further. Was the account privileged? Did the source address appear in other alerts? Was multifactor authentication used? Did the successful login lead to unusual access, data transfers, or changes to account permissions?

The distinction matters because an alert is a signal, not a complete explanation. A failed login sequence may indicate an attack, a user who forgot a password, a misconfigured service, or automated activity that needs more context. A successful login after repeated failures deserves investigation, but the available evidence does not automatically establish that an account was compromised.

How to Practice Without Wasting Hours

Use the objectives to direct your study

Begin with the four CS0-004 domains and their published weightings. The current exam structure lists Security Operations at 34%, Vulnerability Management at 26%, Incident Response and Management at 24%, and Reporting and Communication at 16%.

CS0-004 exam domain weighting
Security Operations 34%
Vulnerability Management 26%
Incident Response and Management 24%
Reporting and Communication 16%

These percentages help you allocate study time, but they should not be treated as a reason to ignore the smaller domain. Reporting and Communication, for example, asks you to turn technical findings into useful information for others. Understanding how to communicate risk and recommend action is part of the analyst’s job, not an optional writing exercise.

For each objective, mark your confidence as strong, uncertain, or unfamiliar. Then test the uncertain topics with targeted questions or practical exercises. If you repeatedly confuse vulnerability severity with real-world exploitability, spend time understanding the distinction rather than completing another broad quiz that mostly tests concepts you already know.

Review mistakes, not just scores

Mock test scores reflect only your performance on specific questions; they fail to reveal the underlying reasons for errors or indicate whether you can flexibly apply the relevant knowledge in other contexts.

Whenever you answer a question incorrectly, make a note of the specific knowledge gap or conceptual misunderstanding that led to the error. Examples include misinterpreting the meaning of a log field, confusing the concepts of "containment" and "eradication," selecting a vulnerability based solely on a high CVSS score, or overlooking a specific detail in the scenario. These are distinct types of issues that require different strategies to address.

You should also review questions you answered correctly merely by guessing. Otherwise, such lucky guesses might mask your weak points, causing the same issues to recur in future questions. Over time, your notes should evolve into a record of your own cognitive pitfalls—especially recurring errors—rather than just a simple compilation of standard explanations.

Build familiarity with security evidence

Reading about a SIEM or vulnerability scanner is useful, but interpreting its output is a different skill. Work with suitable lab exercises that expose you to authentication records, network traffic, endpoint alerts, vulnerability reports, and incident timelines. Practice connecting observations instead of treating every artifact as an isolated fact.

Vulnerability management offers a particularly useful example. A critical CVSS score deserves attention, but prioritization may also depend on whether exploitation is occurring, how important the affected asset is, what exposure exists, and whether an effective remediation is available. The best response is not necessarily to patch the highest-scoring item first without considering context.

Hands-on practice can help you make these distinctions. You do not need to recreate a full enterprise security operations center at home. A carefully chosen exercise that requires you to interpret evidence and justify a decision may teach you more than hours of passive watching.

Use AI as a study assistant, not an authority

AI can help explain unfamiliar concepts, compare related tools, generate extra practice scenarios, or quiz you on an objective. It can also produce plausible explanations that contain technical errors or invent details that were never present in the source material.

A sensible workflow is to select one objective, ask for an explanation and a new hypothetical scenario, answer it yourself, and verify the explanation against reliable documentation. When a response makes a specific claim about a tool, framework, or exam requirement, check the relevant primary source.

AI-assisted study is most useful when it makes you do more reasoning, not when it removes the need to reason. If you cannot explain why an answer is correct without looking at the generated explanation, you have more work to do.

How to Judge Whether a CS0-004 Practice Resource Is Worth Using

A useful resource should help you identify and correct weaknesses. A large question count, polished interface, or confident marketing claim does not establish that a product is well aligned with the current exam.

Evaluate resources using a few practical criteria:

  • Version alignment: Does the material explicitly identify CS0-004, and can you match its coverage to the current objectives?
  • Coverage transparency: Does the provider explain which domains and skills are included, rather than making vague claims about comprehensive preparation?
  • Explanation quality: Do explanations show why an answer fits the evidence and why the alternatives are less suitable?
  • Scenario relevance: Does the material ask you to interpret logs, investigate alerts, evaluate vulnerabilities, or choose response actions where appropriate?
  • Useful feedback: Can you identify recurring weaknesses and decide what to study next?

The transition to V4 makes these checks especially valuable. In recent discussions on Reddit, candidates have described uncertainty about which resources cover CS0-004, while others have emphasized log comprehension and scenario-based reasoning. These are individual experiences, not a representative survey, but they illustrate the practical questions candidates are trying to solve.

You do not necessarily need to buy a completely new library of study materials. If an existing course explains core security concepts well, retain it and use the official objectives to identify missing or changed coverage. Add a version-aligned practice resource or lab only where it addresses a genuine gap.

Candidates evaluating additional exam-preparation material can also review the Leads4Pass CompTIA CySA+ CS0-004 dumps. Check the product details against your preparation needs and the current exam objectives before deciding whether it belongs in your study plan. As with any third-party resource, its value depends on the relevance and quality of the material, not simply on the number of questions available.

The goal is to assemble a manageable combination of structured learning, practical analysis, and feedback that addresses your actual weaknesses.

A Practical Readiness Check Before Exam Day

1.While test scores are important, do not focus on them too narrowly.
During the final sprint, it is advisable to review using fresh case scenarios rather than repeatedly working through old questions where you already know the answers by heart.

2.Your review should cover all four domains; focus on mastering topics you still find challenging and practice articulating your problem-solving rationale—either verbally or in writing. If you cannot explain why one option is superior to others, be sure to revisit the underlying concepts before proceeding.

3.You must also consider your time management when dealing with lengthy case scenarios. The official exam constraints require careful reading, but spending too much time resolving minor uncertainties can leave you short on time for subsequent questions. Practice quickly identifying key evidence, ruling out unsupported conclusions, and moving forward decisively once you have made a well-founded decision.

4.High-quality practice questions serve as a guide and help identify knowledge gaps. Consistent performance, a solid grasp of all tested topics, and the ability to clearly articulate the rationale behind your decisions provide a true reflection of your exam readiness.

Prepare for the Analyst’s Decisions, Not Just the Exam

The strongest CS0-004 preparation plan is not necessarily the most expensive or the most extensive. It is the one that exposes what you do not understand, gives you meaningful opportunities to practice, and helps you correct recurring mistakes.

Start with the current objectives, verify the version of every major resource, and prioritize the skills you cannot yet demonstrate confidently.

Use practice questions to test your understanding rather than memorize outcomes, and treat hands-on exercises as opportunities to connect technical evidence with sound decisions.

If a study resource cannot help you explain why an answer is correct, it is not doing enough on its own. For candidates preparing for CompTIA CySA+ V4, that distinction is worth keeping in mind throughout the entire study process.
CS0-003 Exam Guide: What the CompTIA CySA+ Study Guides Don’t Tell You

The CompTIA CySA+ exam (CS0-003) is a major milestone for cybersecurity professionals, SOC analysts, and IT professionals aiming to elevate their careers. While most study guides cover the basics, there are some key areas that they fail to address — areas that could make or break your success on exam day. In this guide, we’ll explore what you need to know to truly prepare for the CySA+ exam and avoid common pitfalls that many candidates fall into.

Why the CS0-003 Exam Is Harder Than Most People Expect

CS0-003 Exam

The CS0-003 exam isn’t just a memorization test — it’s a real-world assessment of your cybersecurity analysis skills. Most study guides focus on theoretical knowledge, but the exam requires you to think like a Security Operations Center (SOC) analyst. Here’s why the CS0-003 exam is more challenging than many anticipate:

Shift from Theory to Real-World Analysis

Unlike certifications such as Security+, the CySA+ exam requires you to demonstrate the ability to apply security knowledge in real-world scenarios. For example, you won’t just be asked to recall facts about network security. Instead, you will be required to analyze network logs and spot anomalies, a skill that reflects the day-to-day responsibilities of a SOC analyst.

SOC Workflow Thinking

SOC analysts work under pressure, analyzing threats in real-time. The CS0-003 exam evaluates your ability to perform similar tasks, such as identifying malicious activity from a variety of alerts, using security tools to track intruders, and responding to incidents swiftly. The exam doesn’t just test your knowledge — it tests your decision-making process in high-stakes situations.

PBQ Simulations

Performance-based questions (PBQs) are a hallmark of the CySA+ exam. These questions simulate real-world environments where you must use tools and tactics to solve problems, rather than simply recalling facts. You’ll face scenarios like interpreting SIEM (Security Information and Event Management) alerts or analyzing suspicious network traffic, which require critical thinking and analysis.

What the CySA+ CS0-003 Exam Actually Tests

What the CySA+ CS0-003 Exam Actually Tests

The CS0-003 exam is divided into several domains, with each focusing on different aspects of security operations. Here’s a breakdown of what you’ll be tested on:

DomainWeight
Security Operations33%
Vulnerability Management30%
Incident Response20%
Reporting & Communication17%

Why Security Operations Dominates the Exam

Security operations represent the core of the exam. As the largest domain, it accounts for 33% of the total exam weight. This domain emphasizes your ability to monitor, detect, and respond to security events. You’ll need to demonstrate expertise in using common SOC tools and processes to safeguard an organization’s network.

Exam Structure and Scenario-Based Questions

The exam uses a combination of multiple-choice and PBQ formats. The multiple-choice questions test your theoretical knowledge, while PBQs simulate practical scenarios that you would face in a SOC. This structure ensures that you’re not just familiar with security concepts, but also with how to apply them effectively under pressure.

The Biggest Mistake Most CS0-003 Study Guides Make

The Biggest Mistake Most CS0-003 Study Guides Make

Many study guides make the mistake of focusing too much on terminology and memorization. While it’s essential to understand basic concepts, memorizing definitions won’t help you pass the exam. Here’s why:

The Exam Demands Detection Logic and Threat Investigation

The CySA+ exam goes beyond memorization. It tests your ability to apply security analysis skills, such as detecting threats, interpreting logs, and investigating suspicious activity. For instance, you might be asked to examine a SIEM alert and identify whether it’s a false positive or a legitimate threat. Understanding the logic behind detecting these events is far more valuable than memorizing terms.

SIEM Alerts and Network Traffic Analysis

The exam is designed to simulate real-world security monitoring. You might be asked to analyze logs from a SIEM tool or identify indicators of compromise in network traffic. These tasks require a deep understanding of the various tools used in a SOC and how to interpret the data they generate.

Performance-Based Questions: The Real Challenge

Performance-Based Questions:  cs0-003

PBQs are arguably the most challenging part of the CS0-003 exam. While they might seem straightforward, they are designed to test your ability to think critically and act quickly under pressure. Here’s why they’re so difficult:

Log Analysis and Attack Investigation

PBQs often involve analyzing raw logs to determine the nature of an attack. For example, you might need to identify whether a suspicious pattern in network traffic is the result of a DDoS attack or an insider threat. To succeed, you must be familiar with attack vectors and how to spot the early signs of a breach.

Security Tool Configuration and Correlating Events

Another common PBQ scenario involves using tools to identify and correlate security events. You’ll need to demonstrate your knowledge of how different tools interact, as well as how to configure them to provide meaningful data for incident response.

Common PBQ Mistakes

One of the most common mistakes candidates make is treating PBQs like multiple-choice questions. Instead of analyzing the data and considering all possible solutions, many candidates rush to make a decision. This rush often leads to incorrect conclusions, which can severely impact their score.

How Successful Candidates Actually Prepare

cs0-003 exam prep

To truly succeed on the CS0-003 exam, you need to adopt a different study strategy — one that focuses on developing your skills in a SOC environment. Here’s a three-step approach:

Step 1 — Learn SOC Workflows

Understanding how a SOC operates is critical for success. This includes knowledge of tools, workflows, and how analysts collaborate to detect and respond to threats. The exam tests your ability to think like a SOC analyst, so you need to be familiar with real-world scenarios.

Step 2 — Practice Scenario Analysis

Reading through theoretical materials isn’t enough. You need to practice applying your knowledge in real-world scenarios. This can involve using simulation tools, analyzing log files, and working through practice PBQs to build your problem-solving skills.

Step 3 — Use Realistic Practice Questions

Many candidates recommend using curated practice materials that closely mimic the actual exam. One resource that has been popular in the cybersecurity community is Leads4Pass, which offers practice exams designed to simulate the real-world CySA+ experience. These materials provide a more realistic sense of the types of questions you’ll encounter on the actual exam.

Recommended Learning Path for CySA+

If you’re serious about pursuing a career in cybersecurity, the CySA+ exam is an essential stepping stone. Here’s an example of a certification progression to help guide your learning:

LevelCertification
EntrySecurity+
IntermediateCySA+
AdvancedSecurityX

Following this path ensures that you’re building a strong foundation before tackling more advanced certifications like SecurityX (An advanced cybersecurity certification for security architects and senior security engineers.).

Free CS0-003 Practice Questions (PDF)

To help you prepare, I’ve created a free set of CS0-003 practice questions in PDF format. Download the practice questions to test your readiness for the exam and get a feel for the types of questions you’ll face.

Final Thoughts: CS0-003 Is a Security Analyst Exam, Not a Memorization Test

In conclusion, the CS0-003 exam is designed to test your ability to think like a cybersecurity analyst. The exam evaluates your real-world security analysis skills, threat detection capabilities, and incident response thinking. It’s not a memorization test — it’s a hands-on evaluation of your practical knowledge and decision-making ability. To pass, you’ll need to understand SOC workflows, practice real-world scenarios, and develop the critical thinking required to respond to security incidents.

FAQs

  1. How many questions are on the CS0-003 exam?
    The CS0-003 exam contains up to 85 questions, with a mix of multiple-choice and performance-based questions.
  2. What is the passing score for the CySA+ exam?
    The passing score for the CS0-003 exam is 750 out of 900.
  3. Are practice exams helpful for CySA+ preparation?
    Yes, but make sure you use realistic practice exams that simulate the actual test environment, including PBQs.
  4. What tools do I need to be familiar with for the CS0-003 exam?
    Familiarity with SIEM tools, vulnerability management platforms, and incident response tools is essential for the exam.

CS0-002 Dumps [2022] Prep for CompTIA CySA+ Exam

comptia cysa+ exam

[How do I get success on the CS0-002 CompTIA CySA+ exam?]

Using the CS0-002 Dumps is the real learning material for you to successfully pass the CompTIA CySA+ exam.CS0-002 dumps have been updated to include 769 real and valid exam practice questions, we confirm that all CS0-002 exam questions have been verified and reviewed to be authentic and valid to ensure you pass the CS0-002 CompTIA CySA+ exam.

Lead4Pass CS0-002 Dumps is responsible for your real goal of successfully passing the CompTIA CySA+ exam. Visit the CS0-002 Dumps: https://www.leads4pass.com/cs0-002.html.
Achieve a successful first attempt to pass the exam.

[Practice Test] CS0-002 Free Dumps Read First

The questions for CS0-002 were last updated on April 24, 2022.

Viewing questions 1-12 out of 769 questions:

QUESTION 1:

A security analyst has received information from a third-party intelligence-sharing resource that indicates employee accounts were breached. Which of the following is the NEXT step the analyst should take to address the issue?

A. Audit access permissions for all employees to ensure the least privilege.
B. Force a password reset for the impacted employees and revoke any tokens.
C. Configure SSO to prevent passwords from going outside the local network.
D. Set up privileged access management to ensure auditing is enabled.

Correct Answer: B

QUESTION 2:

An organization used a third party to conduct a security audit and discovered several deficiencies in the cybersecurity program. The findings noted many external vulnerabilities that were not caught by the vulnerability scanning software, numerous weaknesses that allowed lateral movement, and gaps in monitoring that did not detect the activity of the auditors. Based on these findings, which of the following would be the BEST long-term enhancement to the security program?

A. Quarterly external penetration testing
B. Monthly tabletop scenarios
C. Red-team exercises
D. Audit exercises

Correct Answer: D

QUESTION 3:

A cybersecurity analyst is supporting an incident response effort via threat intelligence. Which of the following is the analyst MOST likely executing?

A. Requirements analysis and collection planning
B. Containment and eradication
C. Recovery and post-incident review
D. Indicator enrichment and research pivoting

Correct Answer: A

QUESTION 4:

An analyst is participating in the solution analysis process for a cloud-hosted SIEM platform to centralize log monitoring and alerting capabilities in the SOC. Which of the following is the BEST approach for supply chain assessment when selecting a vendor?

A. Gather information from providers, including data center specifications and copies of audit reports.
B. Identify SLA requirements for monitoring and logging.
C. Consult with senior management for recommendations.
D. Perform a proof of concept to identify possible solutions.

Correct Answer: B

QUESTION 5:

In web application scanning, static analysis refers to scanning:

A. the system for vulnerabilities before installing the application.
B. the compiled code of the application to detect possible issues.
C. an application that is installed and active on a system.
D. an application that is installed on a system that is assigned a static IP.

Correct Answer: A
Reference: https://whatis.techtarget.com/definition/static-analysis-static-code-analysis

QUESTION 6:

During an incident, a cybersecurity analyst found several entries in the web server logs that are related to an IP with a bad reputation. Which of the following would cause the analyst to further review the incident?

A. BadReputationIp – – [2019-04-12 10:43Z] “GET /etc/passwd” 403 1023
B. BadReputationIp – – [2019-04-12 10:43Z] “GET /index.html?src=../.ssh/id_rsa” 401 17044
C. BadReputationIp – – [2019-04-12 10:43Z] “GET /a.php?src=/etc/passwd” 403 11056
D. BadReputationIp – – [2019-04-12 10:43Z] “GET /a.php?src=../../.ssh/id_rsa” 200 15036
E. BadReputationIp – – [2019-04-12 10:43Z] “GET /favicon.ico?src=../usr/share/ icons” 200 19064

Correct Answer: D

QUESTION 7:

A company\’s data is still being exfiltered to business competitors after the implementation of a DLP solution. Which of the following is the most likely reason why the data is still being compromised?

A. Printed reports from the database contain sensitive information
B. DRM must be implemented with the DLP solution
C. Users are not labeling the appropriate data sets
D. DLP solutions are only effective when they are implemented with disk encryption

Correct Answer: B
Reference: https://www.vaultize.com/blog/-enterprise-drm-and-dlp-are-amazing-together.html

QUESTION 8:

A large organization wants to move account registration services to the cloud to benefit from faster processing and elasticity. Which of the following should be done FIRST to determine the potential risk to the organization?

A. Establish a recovery time objective and a recovery point objective for the systems being moved
B. Calculate the resource requirements for moving the systems to the cloud
C. Determine recovery priorities for the assets being moved to the cloud-based systems
D. Identify the business processes that will be migrated and the criticality of each one
E. Perform an inventory of the servers that will be moving and assign priority to each one

Correct Answer: D

QUESTION 9:

Which of the following attacks can be prevented by using output encoding?

A. Server-side request forgery
B. Cross-site scripting
C. SQL injection
D. Command injection
E. Cross-site request forgery
F. Directory traversal

Correct Answer: B

QUESTION 10:

During an investigation, a security analyst determines suspicious activity occurred during the night shift over the weekend. Further investigation reveals the activity was initiated from an internal IP going to an external website. Which of the following would be the MOST appropriate recommendation to prevent the activity from happening in the future?

A. An IPS signature modification for the specific IP addresses
B. An IDS signature modification for the specific IP addresses
C. A firewall rule that will block port 80 traffic
D. A firewall rule that will block traffic from the specific IP addresses

Correct Answer: D

QUESTION 11:

The Chief Information Officer (CIO) for a large manufacturing organization has noticed a significant number of unknown devices with possible malware infections are on the organization\’s corporate network. Which of the following would work BEST to prevent the issue?

A. Reconfigure the NAC solution to prevent access based on a full device profile and ensure antivirus is installed.
B. Segment the network to isolate all systems that contain highly sensitive information, such as intellectual property.
C. Implement certificate validation on the VPN to ensure only employees with the certificate can access the company network.
D. Update the antivirus configuration to enable behavioral and real-time analysis on all systems within the network.

Correct Answer: A

QUESTION 12:

A development team is testing a new application release. The team needs to import existing client PHI data records from the production environment to the test environment to test accuracy and functionality. Which of the following would BEST protect the sensitivity of this data while still allowing the team to perform the testing?

A. Deidentification
B. Encoding
C. Encryption
D. Watermarking

Correct Answer: A

……


[Google Drive] CS0-002 Free Dumps Online Download:https://drive.google.com/file/d/1bsSyU7x5kxHDZv6gKqUgh6IMMz_B75ZS/view?usp=sharing

[Why Choose Lead4Pass CS0-002 Dumps?]

Lead4Pass CS0-002 Dumps comes with both PDF and VCE study tools to help you study easily and quickly pass the CompTIA CySA+ exam in a variety of environments.769 complete CS0-002 dumps questions can be obtained at the address: https://www.leads4pass.com/cs0-002.html. Congratulations in advance on your success.

How to successfully pass the CompTIA CS0-002 exam

You can choose the online practice test on this site to successfully pass the exam. Studying here can improve your exam pass rate! Of course, you can also choose Lead4Pass CS0-002 dumps https://www.leads4pass.com/cs0-002.html (PDF + VCE). Lead4Pass contains complete exam questions and answers.
It has a 99.5% exam pass rate! Help you pass the exam easily.

Share the CompTIA CS0-002 exam PDF for free

The freely shared CompTIA CS0-002 exam PDF is only part of the Lead4Pass CS0-002 exam questions and answers.
The free exam PDF can help you understand the latest and updated CompTIA CS0-002 exam content. I recommend Lead4Pass to pass the CS0-002 exam.

CompTIA CS0-002 online practice test

QUESTION 1
An organization developed a comprehensive incident response policy. Executive management approved the policy and
its associated procedures. Which of the following activities would be MOST beneficial to evaluate personnel\\’s
familiarity with incident response procedures?
A. A simulated breach scenario involving the incident response team
B. Completion of annual information security awareness training by all employees
C. Tabletop activities involving business continuity team members
D. Completion of lessons-learned documentation by the computer security incident response team
E. External and internal penetration testing by a third party
Correct Answer: A


QUESTION 2
A company\\’s Chief Information Security Officer (CISO) is concerned about the integrity of some highly confidential
files. Any changes to these files must be tied back to a specific authorized user\\’s activity session. Which of the
following is the BEST technique to address the CISO\\’s concerns?
A. Configure DLP to reject all changes to the files without pre-authorization. Monitor the files for unauthorized changes.
B. Regularly use SHA-256 to hash the directory containing the sensitive information. Monitor the files for unauthorized
changes.
C. Place a legal hold on the files. Require authorized users to abide by a strict time context access policy.Monitor the
files for unauthorized changes.
D. Use Wireshark to scan all traffic to and from the directory. Monitor the files for unauthorized changes.
Correct Answer: A


QUESTION 3
A security analyst is building a malware analysis lab. The analyst wants to ensure malicious applications are not
capable of escaping the virtual machines and pivoting to other networks. To BEST mitigate this risk, the analyst should
use __________.
A. an 802.11ac wireless bridge to create an air gap.
B. a managed switch to segment the lab into a separate VLAN.
C. a firewall to isolate the lab network from all other networks.
D. an unmanaged switch to segment the environments from one another.
Correct Answer: C


QUESTION 4
A small organization has proprietary software that is used internally. The system has not been well maintained and
cannot be updated with the rest of the environment Which of the following is the BEST solution?
A. Virtualize the system and decommission the physical machine.
B. Remove it from the network and require air gapping.
C. Only allow access to the system via a jumpbox
D. Implement MFA on the specific system.
Correct Answer: A


QUESTION 5
The inability to do remote updates of certificates. keys software and firmware is a security issue commonly associated
with:
A. web servers on private networks.
B. HVAC control systems
C. smartphones
D. firewalls and UTM devices
Correct Answer: B


QUESTION 6
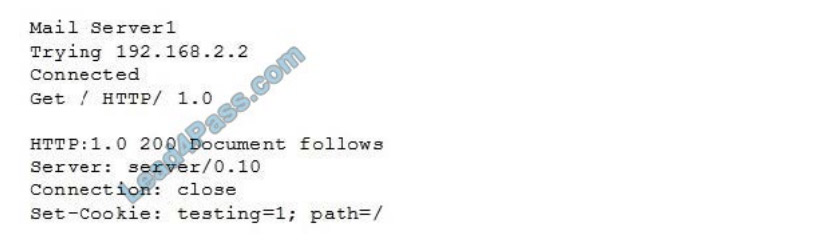
A cybersecurity analyst is currently checking a newly deployed server that has an access control list applied. When
conducting the scan, the analyst received the following code snippet of results:comptia cs0-002 exam questions q6

Which of the following describes the output of this scan?
A. The analyst has discovered a False Positive, and the status code is incorrect providing an OK message.
B. The analyst has discovered a True Positive, and the status code is correct providing a file not found error message.
C. The analyst has discovered a True Positive, and the status code is incorrect providing a forbidden message.
D. The analyst has discovered a False Positive, and the status code is incorrect providing a server error message.
Correct Answer: B


QUESTION 7
A company\\’s modem response team is handling a threat that was identified on the network Security analysts have as
at remote sites. Which of the following is the MOST appropriate next step in the incident response plan?
A. Quarantine the web server
B. Deploy virtual firewalls
C. Capture a forensic image of the memory and disk
D. Enable web server containerization
Correct Answer: B


QUESTION 8
Which of the following software assessment methods would be BEST for gathering data related to an application\\’s
availability during peak times?
A. Security regression testing
B. Stress testing
C. Static analysis testing
D. Dynamic analysis testing
E. User acceptance testing
Correct Answer: B


QUESTION 9
A malicious hacker wants to gather guest credentials on a hotel 802.11 network. Which of the following tools is the
malicious hacker going to use to gain access to information found on the hotel network?
A. Nikto
B. Aircrak-ng
C. Nessus
D. tcpdump
Correct Answer: A


QUESTION 10
A security analyst is reviewing the following web server log:
GET %2f..%2f..%2f.. %2f.. %2f.. %2f.. %2f../etc/passwd
Which of the following BEST describes the issue?
A. Directory traversal exploit
B. Cross-site scripting
C. SQL injection
D. Cross-site request forgery
Correct Answer: A


QUESTION 11
A company\\’s senior human resources administrator left for another position, and the assistant administrator was
promoted into the senior position. On the official start day, the new senior administrator planned to ask for extended
access permissions but noticed the permissions were automatically granted on that day. Which of the following
describes the access management policy in place at the company?
A. Mandatory-based
B. Host-based
C. Federated access
D. Role-based
Correct Answer: D


QUESTION 12
Which of the following should a database administrator implement to BEST protect data from an untrusted server
administrator?
A. Data deidentification
B. Data encryption
C. Data masking
D. Data minimization
Correct Answer: B


QUESTION 13
Employees of a large financial company are continuously being Infected by strands of malware that are not detected by
EDR tools. When of the following Is the BEST security control to implement to reduce corporate risk while allowing
employees to exchange files at client sites?
A. MFA on the workstations
B. Additional host firewall rules
C. VDI environment
D. Hard drive encryption
E. Network access control
F. Network segmentation
Correct Answer: B


QUESTION 14
A security analyst is reviewing vulnerability scan results and notices new workstations are being flagged as having
outdated antivirus signatures. The analyst observes the following plugin output:
Antivirus is installed on the remote host:
Installation path: C:\Program Files\AVProduct\Win32\
Product Engine: 14.12.101
Engine Version: 3.5.71
Scanner does not currently have information about AVProduct version 3.5.71. It may no longer be supported.
The engine version is out of date. The oldest supported version from the vendor is 4.2.11. The analyst uses the
vendor\\’s website to confirm the oldest supported version is correct.
Which of the following BEST describes the situation?
A. This is a false positive, and the scanning plugin needs to be updated by the vendor.
B. This is a true negative, and the new computers have the correct version of the software.
C. This is a true positive, and the new computers were imaged with an old version of the software.
D. This is a false negative, and the new computers need to be updated by the desktop team.
Correct Answer: C


QUESTION 15
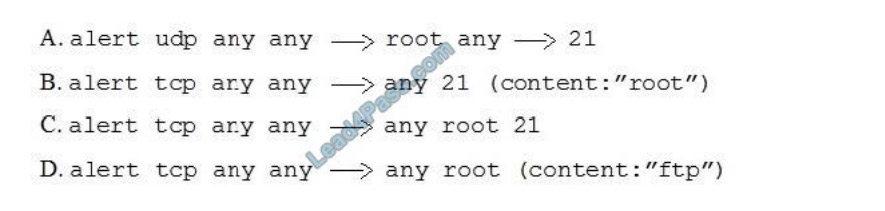
A security administrator needs to create an IDS rule to alert on FTP login attempts by root. Which of the following rules
is the BEST solution?comptia cs0-002 exam questions q15

A. Option A
B. Option B
C. Option C
D. Option D
Correct Answer: B


The freely shared CompTIA CS0-002 exam questions and answers are the latest updates to help you understand the latest exam questions.
All questions and answers are carefully shared by us for free! To easily pass the exam,
please choose the complete CompTIA CS0-002 exam dumps https://www.leads4pass.com/cs0-002.html (Total Questions: 260 Q&A).
All questions and answers are up-to-date to ensure that you receive a notification of successful certification after the exam.

ps.

The freely shared CompTIA CS0-002 exam PDF is only part of the Lead4Pass CS0-002 exam questions and answers. The free exam PDF can help you understand the latest and updated CompTIA CS0-002 exam content.
I recommend Lead4Pass to pass the CS0-002 exam.

[2021.6 Updated] Valid Leads4Pass CompTIA CS0-002 exam questions with VCE and PDF download

New updated CompTIA CS0-002 exam questions from Lead4Pass CompTIA CS0-002 dumps!
Welcome to download the latest Lead4Pass CompTIA CS0-002 dumps with PDF and VCE: https://www.leads4pass.com/cs0-002.html (260 Q&As)

[CompTIA CS0-002 exam pdf] CompTIA CS0-002 exam PDF uploaded from google drive, online download provided by the latest update of Lead4pass:
https://drive.google.com/file/d/1c4cmZiff661oldNP09QBlTZMvUEPe755/

Latest update CompTIA CS0-002 exam questions and answers online practice test

QUESTION 1
An information security analyst is working with a data owner to identify the appropriate controls to preserve the
confidentiality of data within an enterprise environment One of the primary concerns is the exfiltration of data by malicious
insiders, Which of the following controls is the MOST appropriate to mitigate risks?
A. Data deduplication
B. OS fingerprinting
C. Digital watermarking
D. Data loss prevention
Correct Answer: D

QUESTION 2
A company\\’s modem response team is handling a threat that was identified on the network Security analysts have as
at remote sites. Which of the following is the MOST appropriate next step in the incident response plan?
A. Quarantine the webserver
B. Deploy virtual firewalls
C. Capture a forensic image of the memory and disk
D. Enable webserver containerization
Correct Answer: B

QUESTION 3
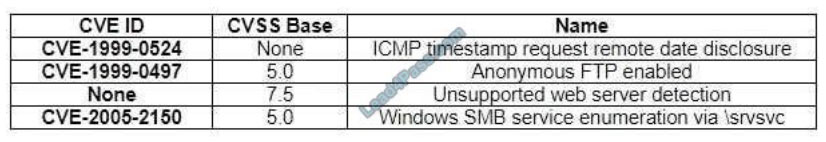
A security analyst, who is working for a company that utilizes Linux servers, receives the following results from a
vulnerability scan:comptia cs0-002 certification exam q3

Which of the following is MOST likely a false positive?
A. ICMP timestamp request remote data disclosure
B. Windows SMB service enumeration via \srvsvc
C. Anonymous FTP enabled
D. Unsupported web server detection
Correct Answer: B

QUESTION 4
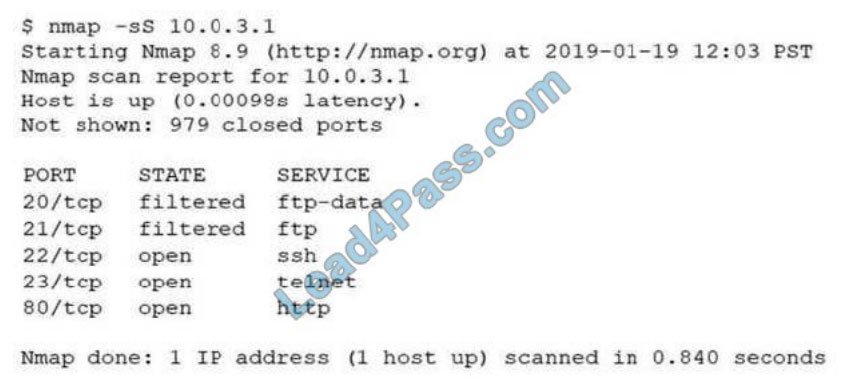
An analyst performs a routine scan of a host using Nmap and receives the following output:comptia cs0-002 certification exam q4

Which of the following should the analyst investigate FIRST?
A. Port 21
B. Port 22
C. Port 23
D. Port 80
Correct Answer: C

QUESTION 5
A Chief Information Security Officer (CISO) is concerned the development team, which consists of contractors, has too
much access to customer data
Developers use personal workstations, giving the company little to no visibility into the development activities.
Which of the following would be BEST to implement to alleviate the CISO\\’s concern?
A. DLP
B. Encryption
C. Test data
D. NDA
Correct Answer: D

QUESTION 6
A security analyst received an alert from the SIEM indicating numerous login attempts from users outside their usual
geographic zones, all of which were initiated through the web-based mail server. The logs indicate all domain accounts
experienced two login attempts during the same time frame. Which of the following is the MOST likely cause of this
issue?
A. A password-spraying attack was performed against the organization.
B. A DDoS attack was performed against the organization.
C. This was normal shift work activity; the SIEM\\’s AI is learning.
D. A credentialed external vulnerability scan was performed.
Correct Answer: A
Reference: https://doubleoctopus.com/security-wiki/threats-and-tools/password-spraying/

QUESTION 7
Which of the following attacks can be prevented by using output encoding?
A. Server-side request forgery
B. Cross-site scripting
C. SQL injection
D. Command injection
E. Cross-site request forgery
F. Directory traversal
Correct Answer: B

QUESTION 8
A small electronics company decides to use a contractor to assist with the development of a new FPGA- based device.
Several of the development phases will occur off-site at the contractor\\’s labs. Which of the following is the main
concern a security analyst should have with this arrangement?
A. Making multiple trips between development sites increases the chance of physical damage to the FPGAs.
Latest CS0-002 Dumps | CS0-002 PDF Dumps | CS0-002 VCE Dumps 4 / 7
https://www.leads4pass.com/CS0-002.html
2021 Latest lead4pass CS0-002 PDF and VCE dumps Download
B. Moving the FPGAs between development sites will lessen the time that is available for security testing.
C. Development phases occurring at multiple sites may produce change management issues.
D. FPGA applications are easily cloned, increasing the possibility of intellectual property theft.
Correct Answer: B
Reference: https://www.eetimes.com/how-to-protect-intellectual-property-in-fpgas-devices-part-1/#

QUESTION 9
Employees of a large financial company are continuously being Infected by strands of malware that are not detected by
EDR tools. When of the following Is the BEST security control to implement to reduce corporate risk while allowing
employees to exchange files at client sites?
A. MFA on the workstations
B. Additional host firewall rules
C. VDI environment
D. Hard drive encryption
E. Network access control
F. Network segmentation
Correct Answer: B

QUESTION 10
Which of the following technologies can be used to house the entropy keys for task encryption on desktops and
laptops?
A. Self-encrypting drive
B. Bus encryption
C. TPM D. HSM
Correct Answer: A

QUESTION 11
An organization needs to limit its exposure to accidental disclosure when employees send emails that contain personal
information to recipients outside the company Which of the following technical controls would BEST accomplish this
goal?
A. DLP
B. Encryption
C. Data masking
D. SPF
Correct Answer: A

QUESTION 12
A security analyst suspects a malware infection was caused by a user who downloaded malware after clicking
http:///a.php is a phishing email.
To prevent other computers from being infected by the same malware variation, the analyst should create a rule on the
__________.
A. email server that automatically deletes attached executables.
B. IDS to match the malware sample.
C. proxy to block all connections to.
D. firewall to block connection attempts to dynamic DNS hosts.
Correct Answer: C

QUESTION 13
As part of a review of incident response plans, which of the following is MOST important for an organization to
understand when establishing the breach notification period?
A. Organizational policies
B. Vendor requirements and contracts
C. Service-level agreements
D. Legal requirements
Correct Answer: D


The above content: shared CS0-002 exam pdf, CS0-002 Exam Questions And Answers, CS0-002 exam video, and get the complete CS0-002 exam dump path.
For information about CS0-002 Dumps from Lead4pass (including PDF and VCE), please visit: https://www.leads4pass.com/cs0-002.html (260 Q&A)

ps.
Get free CompTIA CS0-002 dumps PDF online: https://drive.google.com/file/d/1c4cmZiff661oldNP09QBlTZMvUEPe755/

[MAR 2021] CompTIA CS0-002 exam dumps and online practice questions are available from Leads4Pass

The latest updated CompTIA CS0-002 exam dumps and free CS0-002 exam practice questions and answers! Latest updates from Lead4Pass CompTIA CS0-002 Dumps PDF and CS0-002 Dumps VCE, Lead4Pass CS0-002 exam questions updated and answers corrected!
Get the full CompTIA CS0-002 dumps from https://www.leads4pass.com/cs0-002.html (VCE&PDF)

Latest CS0-002 PDF for free

Share the CompTIA CS0-002 Dumps PDF for free From Lead4pass CS0-002 Dumps part of the distraction collected on Google Drive shared by Lead4pass
https://drive.google.com/file/d/1XuTVvaCEqjkY-h0L_DQCfSH1B_Y061Sd/

The latest updated CompTIA CS0-002 Exam Practice Questions and Answers Online Practice Test is free to share from Lead4Pass (Q1-Q13)

QUESTION 1
An audit has revealed an organization is utilizing a large number of servers that are running unsupported operating
systems.
As part of the management response phase of the audit, which of the following would BEST demonstrate senior
management is appropriately aware of and addressing the issue?
A. Copies of prior audits that did not identify the servers as an issue
B. Project plans relating to the replacement of the servers that were approved by management
C. Minutes from meetings in which risk assessment activities addressing the servers were discussed
D. ACLs from perimeter firewalls showing blocked access to the servers
E. Copies of change orders relating to the vulnerable servers
Correct Answer: C

QUESTION 2
A security analyst is responding to an incident on a web server on the company network that is making a large number
of outbound requests over DNS Which of the following is the FIRST step the analyst should take to evaluate this potential indicator of compromise\\’?
A. Run an anti-malware scan on the system to detect and eradicate the current threat
B. Start a network capture on the system to look into the DNS requests to validate command and control traffic.
C. Shut down the system to prevent further degradation of the company network
D. Reimage the machine to remove the threat completely and get back to a normal running state.
E. Isolate the system on the network to ensure it cannot access other systems while evaluation is underway.
Correct Answer: A

QUESTION 3
An analyst has been asked to provide feedback regarding the controls required by a revised regulatory framework. At
this time, the analyst only needs to focus on the technical controls.
Which of the following should the analyst provide an assessment of?
A. Tokenization of sensitive data
B. Establishment of data classifications
C. Reporting on data retention and purging activities
D. Formal identification of data ownership
E. Execution of NDAs
Correct Answer: A

QUESTION 4
A security analyst is reviewing the following log entries to identify anomalous activity:[2021.3] lead4pass cs0-002 practice test q4

Which of the following attack types is occurring?
A. Directory traversal
B. SQL injection
C. Buffer overflow
D. Cross-site scripting
Correct Answer: A

QUESTION 5
A security analyst is investigating a compromised Linux server. The analyst issues the ps command and receives the
following output:[2021.3] lead4pass cs0-002 practice test q5

Which of the following commands should the administrator run NEXT to further analyze the compromised system?
A. strace /proc/1301
B. rpm -V openash-server
C. /bin/la -1 /proc/1301/exe
D. kill -9 1301
Correct Answer: A

QUESTION 6
A security analyst is investigating a system compromise. The analyst verifies the system was up to date on OS patches
at the time of the compromise. Which of the following describes the type of vulnerability that was MOST likely
exploited?
A. Insider threat
B. Buffer overflow
C. Advanced persistent threat
D. Zero-day
Correct Answer: D

QUESTION 7
An analyst is investigating an anomalous event reported by the SOC. After reviewing the system logs, the analyst
identifies an unexpected addition of a user with root-level privileges on the endpoint. Which of the following data sources
will BEST help the analyst to determine whether this event constitutes an incident?
A. Patching logs
B. Threat feed
C. Backup logs
D. Change requests
E. Data classification matrix
Correct Answer: E

QUESTION 8
An analyst identifies multiple instances of node-to-node communication between several endpoints within the
10.200.2.0/24 network and a user machine at the IP address 10.200.2.5. This user machine at the IP address
10.200.2.5 is also identified as initiating outbound communication during atypical business hours with several IP
addresses that have recently appeared on threat feeds.
Which of the following can be inferred from this activity?
A. 10.200.2.0/24 is infected with ransomware.
B. 10.200.2.0/24 is not routable address space.
C. 10.200.2.5 is a rogue endpoint.
D. 10.200.2.5 is exfiltrating data.
Correct Answer: D

QUESTION 9
Which of the following BEST describes the process by which code is developed, tested, and deployed in small
batches?
A. Agile
B. Waterfall
C. SDLC
D. Dynamic code analysis
Correct Answer: C
Reference: https://www.cleverism.com/software-development-life-cycle-sdlc-methodologies/

QUESTION 10
A network attack that is exploiting a vulnerability in the SNMP is detected. Which of the following should the
cybersecurity analysts do FIRST?
A. Apply the required patches to remediate the vulnerability.
B. Escalate the incident to senior management for guidance.
C. Disable all privileged user accounts on the network.
D. Temporarily block the attacking IP address.
Correct Answer: A
Reference: https://beyondsecurity.com/scan-pentest-network-vulnerabilities-snmp-protocol-version-detection.html

QUESTION 11
As part of a merger with another organization, a Chief Information Security Officer (CISO) is working with an assessor to
perform a risk assessment focused on data privacy compliance. The CISO is primarily concerned with the potential legal
liability and fines associated with data privacy. Based on the CISO\\’s concerns, the assessor will MOST likely focus on:
A. qualitative probabilities.
B. quantitative probabilities.
C. qualitative magnitude.
D. quantitative magnitude.
Correct Answer: D

QUESTION 12
The security team at a large corporation is helping the payment-processing team to prepare for a regulatory compliance
audit and meet the following objectives:
1.
Reduce the number of potential findings by the auditors.
2.
Limit the scope of the audit to only devices used by the payment-processing team for activities directly impacted by the
regulations.
3.
Prevent the external-facing web infrastructure used by other teams from coming into the scope.
4.
Limit the amount of exposure the company will face if the systems used by the payment-processing team are
compromised.
Which of the following would be the MOST effective way for the security team to meet these objectives?
A. Limit the permissions to prevent other employees from accessing data owned by the business unit.
B. Segment the servers and systems used by the business unit from the rest of the network.
C. Deploy patches to all servers and workstations across the entire organization.
D. Implement full-disk encryption on the laptops used by employees of the payment-processing team.
Correct Answer: B

QUESTION 13
When attempting to do a stealth scan against a system that does not respond to ping, which of the following Nmap
commands BEST accomplishes that goal?
A. Nmap -SA -O -noping
B. Nmap -sT -O -P0
C. Nmap -sS -O -P0
D. Nmap -SQ -O -P0
Correct Answer: C


Fulldumps shares the latest updated CompTIA CS0-002 exam exercise questions, CS0-002 dumps pdf for free.
All exam questions and answers come from the Lead4pass exam dumps shared part! Lead4pass updates throughout the year and shares a portion of your exam questions for free to help you understand the exam content and enhance your exam experience!
Get the full CompTIA CS0-002 exam dumps questions at https://www.leads4pass.com/cs0-002.html (pdf&vce)

ps.
Get free CompTIA CS0-002 dumps PDF online: https://drive.google.com/file/d/1XuTVvaCEqjkY-h0L_DQCfSH1B_Y061Sd/